iBankCoin

New ECB Tier One Capital Rules for Monte Paschi Spells Trouble For Deutsche Bank and Others

The Monte Paschi saga continues. If we lives in normal times, they’d like the rotten bank go bankrupt already. After all, the bank sucks. But since we live in an era of perpetual bailouts led by central banks, Monte Paschi gets to live and infect many others with its disease.

Yesterday the ECB announced new rules for Monte, demanding that the prospective Italian bailout of the bank bring its tier one capital up to 8% from the current -2.4%.

Jesus Christ.

Currently the legal minimum is 4.5%. If the ECB were to hold other European banks to the 8% standard, well then, at least 10 of them will need to raise new capital, including Deutsche Bank, Unicredit and Allied Irish.

“There’s a lot more to be explained,” said John Raymond, senior European bank analyst at CreditSights. “They just say, ‘Oh, this is needed to get to 8 percent,’ as if we all knew the number was 8 percent, when in fact that’s a completely new number.”

Monte Paschi needs to raise at least $9b, hardly any of which will come from the private sector. The Italian government will have to bail them out.

Based on the recent stress test, Allied Irish had a CET1 ratio of 4.3%, Deutsche Bank 7.8%, Unicredit 7.1%, Barclays 7.3% and Soc Gen 7.5%.

Comments »

Putin Responds to Obama’s Sanctions by Inviting American Diplomats and Their Families in Russia to New Year’s Celebrations at the Kremlin

Vladimir Putin was responded to US sanctions, which gave Russian diplomats and their families in America 72 hrs to leave America soil, just prior to the New Year’s by graciously inviting American diplomats and their children to the Kremlin for champagne and fine foods, to enjoy New Year’s festivities.

Jesus Christ this much piss Obama off to no end.

Vlad’s letter to Barry.

We regard the recent unfriendly steps taken by the outgoing US administration as provocative and aimed at further weakening the Russia-US relationship. This runs contrary to the fundamental interests of both the Russian and American people. Considering the global security responsibilities of Russia and the United States, this is also damaging to international relations as a whole.

As it proceeds from international practice, Russia has reasons to respond in kind. Although we have the right to retaliate, we will not resort to irresponsible ‘kitchen’ diplomacy but will plan our further steps to restore Russian-US relations based on the policies of the Trump Administration.

The diplomats who are returning to Russia will spend the New Year’s holidays with their families and friends. We will not create any problems for US diplomats. We will not expel anyone. We will not prevent their families and children from using their traditional leisure sites during the New Year’s holidays. Moreover, I invite all children of US diplomats accredited in Russia to the New Year and Christmas children’s parties in the Kremlin.

It is regrettable that the Obama Administration is ending its term in this manner. Nevertheless, I offer my New Year greetings to President Obama and his family.

My season’s greetings also to President-elect Donald Trump and the American people.

I wish all of you happiness and prosperity.

Checkmate.

Comments »

John McAfee: ‘I Can Guarantee You, It Was Not the Russians’

In case some of you were duped into believing this was evidence that proved Russia hacked the US elections, John McAfee would like to remind you that you’re probably a high tier retard and would believe virtually anything your government told you.

Crazy, but brilliant, John said “if it looks like the Russians did it, then I can guarantee you it was not the Russians.”

The Joint Analysis Report from the FBI contains an appendix that lists hundreds of IP addresses that were supposedly “used by Russian civilian and military intelligence services.” While some of those IP addresses are from Russia, the majority are from all over the world, which means that the hackers constantly faked their location.

McAfee argues that the report is a “fallacy,” explaining that hackers can fake their location, their language, and any markers that could lead back to them. Any hacker who had the skills to hack into the DNC would also be able to hide their tracks, he said

“If I was the Chinese and I wanted to make it look like the Russians did it, I would use Russian language within the code, I would use Russian techniques of breaking into the organization,” McAfee said, adding that, in the end, “there simply is no way to assign a source for any attack.”

However, McAfee does see a problem with the National Security Agency (NSA) being able to listen in on every conversation and read every text message and email of every American. Rather than focusing on disrupting the bad guys in foreign countries, McAfee thinks that “all of that effort has been placed on a country that is afraid of its own citizens.”

He claims that the only way he has been able to fully block the NSA from infecting his phone with spyware is by using a flip-phone too old to be hacked. He even goes as far as to call the iPhone the “ultimate spy device.”

Since the stakes are so high, thermonuclear war and all, the least the CIA and other wonderful intelligence agencies can do is provide sufficient evidence to the American people before they get annihilated under the winds of a 10,000 degree winter breeze. Or is that too much to ask? Judging by just about everything they’ve told us over the past 15 years, I’m inclined to believe the exact opposite is true.

Kim dot Com agrees with McAfee’s assertions. This isn’t exactly rocket science.

Comments »

DRUDGE REPORT HIT WITH MASSIVE DDOS ATTACK; MATT DRUDGE PONDERS IF GOVERNMENT WAS BEHIND ATTACK

Drudgereport.com was the number 1 source of information during the elections. It was and always has been, or at least for the past decade or so, the single most popular destination for news — especially during elections. On the same day that the Obama administration announced sanctions again Russia, Drudge goes down.

Coincidence?

Drudge ponders aloud on Twitter.

down

One of my favorite interviews ever was when Drudge showed up to the Alex Jones show for a chat.

Comments »

Attention Exodus Members: The New GARP Index Has Been Launched

Pardon the late night, late year self-indulgence. We do need to keep the champagne flowing around here and have worked very hard at keeping Exodus a top tier information tool for investors. I just launched the new GARP index for the first half of 2017 and it’s probably my boldest yet. I can’t give any details away to non-members, since your sort do not possess such privileges, but just know that I placed a lot of effort behind it.

As God is my witness, it will likely return -100% over the next six months. Nonetheless, I’ve prepared myself for extreme winship in 2017. After a year traveling the seven seas in an ark filled with gay giraffes and attack cobras, I’ve earned the right, by natural law, to return to my former glory and grace — imbued with the powers of 10,000 men and the brains of a billion — to set forth into the stock exchange and to remove the money from others and gently place it into my own pockets.

To all those interested in crossing my path, or to obstruct me in any way humanly possible, just know that I will crush and smother you — rip your skin from your skeletal bones — crown to toe — and then grind your bones into dust to be used in my summer gardens.

The GARP INDEX, gentlemen.

Comments »

Elysium: Chinese IPOs Returned Nearly 400% in First Month of Trading During 2016

This is not as bubble, but a renaissance. The glorious Chinese people are adorned with the best of things — the prettiest and mightiest repurposed Soviet era aircraft carriers and the best stocks money could buy.

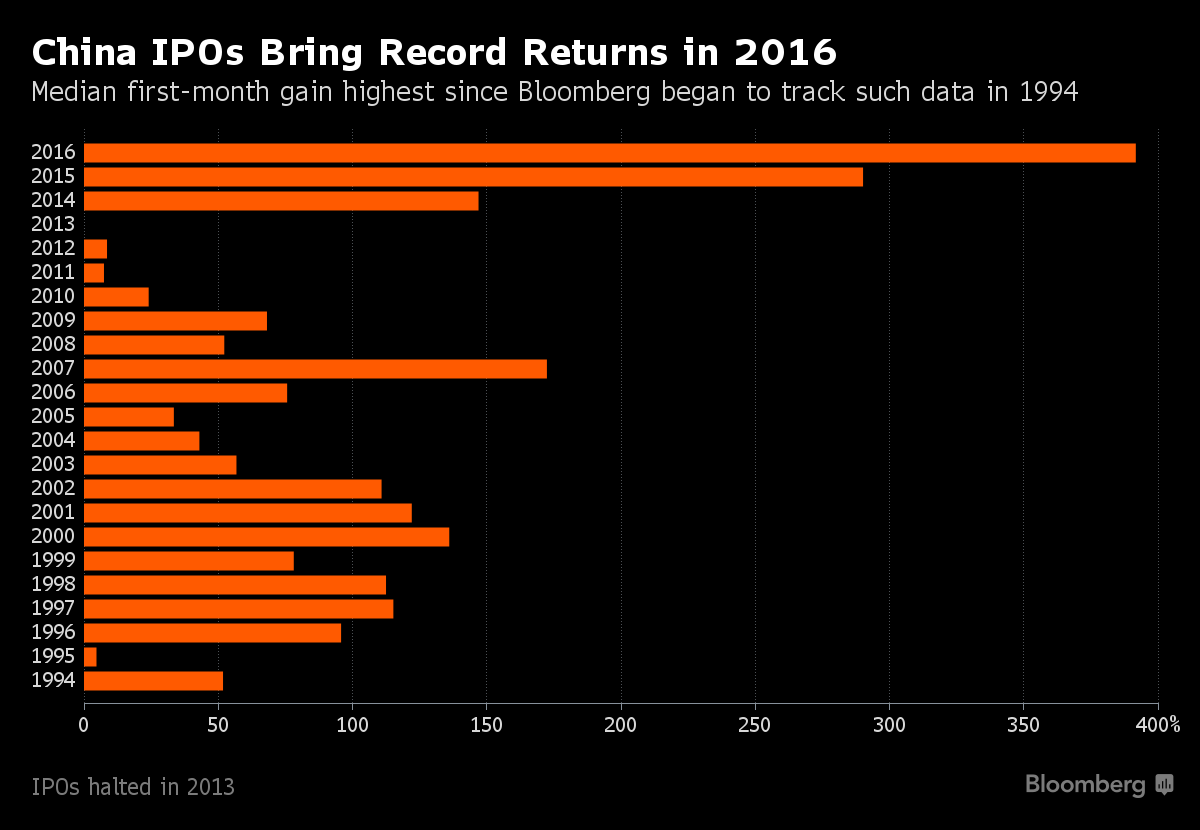
Over the course of 2016, mainland Chinese IPOs returned a mere 392% during the first month of trade — a mere pittance for such a wonderfully decadent society of dog eating swill drinkers.

It’s worth noting, the Chinese IPO market is a hard nut to crack. Similar to the United States, where preferred clientele at Goldman and JP Morgan get the bulk of the allocation, you have to be well connected and rich to get one in China. Bloomberg places the odds of getting an IPO at China 1 in 2,500, but I’m positive that’s a bullshit number — disseminated by enemy propaganda.

It’s much, much higher.

Two hundred and twenty six companies went public in China this year, the most since 2011, and the MEDIAN return was 392%.

The fuck out of here with this shit, right?

not-a-bubble

Meanwhile, the Shanghai sucked some major dick, off by 12%.

“In a weak market, speculators crowd into new shares where they believe selling pressure is low,” said Zhang Haidong, chief strategist at Jinkuang Investment Management in Shanghai.

Oh, you don’t say? That’s what happened, a flight to inequality so to say.

In case you’re wondering how in the world 226 stocks yielded a median return of 392%, the answer lies in the rules set forth by the government in Beijing. If you’re interested in tapping capital markets, you may not bring your company public unless it’s valuation is below 23x earnings. Where did such a precise number of 23x earnings come from? No one knows. Most likely from one of the whores or mistresses of any number of Chinese government officials.

The average IPO size was $106m. In other words, China’s ipo market is a rigged system of penny stock shit offerings.


Comments »

Russia Responds to Sanctions, says Obama’s ‘Aggressive Foreign Policy’ Designed to Hurt Trump

Under normal circumstances, the President-elect Trump and President Obama would discuss the proposed sanctions on Russia and issue a joint statement. After all, Obama doesn’t have to deal with the ramifications, Trump does. But in this fucked up political environment we live in, the incoming President and the one sitting in the White House agree on virtually nothing.

Obama and the democrats believe Russia won the election for Trump. As a matter of fact, many republicans like McCain and Ryan most likely believe the same. As such, we have a delicate situation playing out where Russia is being punished and publicly humiliated, in spite of the wishes of the President elect.

The spokesman for President Vladimir Putin says Moscow regrets the new sanctions that the Obama administration imposed on Russia on Thursday and is considering retaliatory steps.

Dmitry Peskov, spokesman for the Kremlin, said Obama’s actions were both “unpredictable” and “aggressive foreign policy.”

He furthered:

“Such steps of the U.S. administration that has three weeks left to work are aimed at two things: to further harm Russian-American ties, which are at a low point as it is, as well as, obviously, deal a blow on the foreign policy plans of the incoming administration of the president-elect.”

Peskov said Putin was working on methods to retaliate.

Konstantin Kosachev, head of the Kremlin’s upper house’s international affairs committee, told Interfax  Russia “needs to consider the circumstances of the transition period and a possible reaction of the U.S. president-elect.”


Comments »

The FBI and DHS Issue Report Showing Juvenile Evidence of Russian Hacking

Are they seriously going to claim this 3-page report proves Russia hacked our elections?

Here are the juicy details, highlighted by retarded graphics, showing ‘adversary, neutral, and VICTIM spaces.’ In this ‘report’, the government claims Russian agents, labeled APT28 and APT29, hacked into a US political party. These hackers, apparently, have a long track record of hacking into governments, universities, think tanks, and corporations — on a global scale.
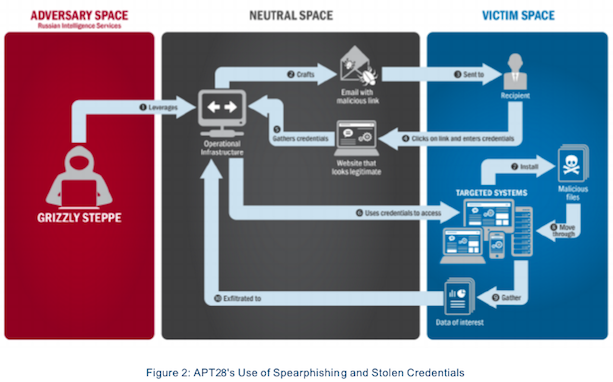
proof

Previous JARs have not attributed malicious cyber activity to specific countries or threat actors. However, public attribution of these activities to RIS is supported by technical indicators from the U.S. Intelligence Community, DHS, FBI, the private sector, and other entities. This determination expands upon the Joint Statement released October 7, 2016, from the Department of Homeland Security and the Director of National Intelligence on Election Security. This activity by RIS is part of an ongoing campaign of cyber-enabled operations directed at the U.S. government and its citizens.

These cyber operations have included spearphishing campaigns targeting government organizations, critical infrastructure entities, think tanks, universities, political organizations, and corporations leading to the theft of information. In foreign countries, RIS actors conducted damaging and/or disruptive cyber-attacks, including attacks on critical infrastructure networks. In some cases, RIS actors masqueraded as third parties, hiding behind false online personas designed to cause the victim to misattribute the source of the attack. This JAR provides technical indicators related to many of these operations, recommended mitigations, suggested actions to take in response to the indicators provided, and information on how to report such incidents to the U.S. Government.

The U.S. Government confirms that two different RIS actors participated in the intrusion into a U.S. political party. The first actor group, known as Advanced Persistent Threat (APT) 29, entered into the party’s systems in summer 2015, while the second, known as APT28, entered in spring 2016.

Both groups have historically targeted government organizations, think tanks, universities, and corporations around the world. APT29 has been observed crafting targeted spearphishing campaigns leveraging web links to a malicious dropper; once executed, the code delivers Remote Access Tools (RATs) and evades detection using a range of techniques. APT28 is known for leveraging domains that closely mimic those of targeted organizations and tricking potential victims into entering legitimate credentials. APT28 actors relied heavily on shortened URLs in their spearphishing email campaigns.

Once APT28 and APT29 have access to victims, both groups exfiltrate and analyze information to gain intelligence value. These groups use this information to craft highly targeted spearphishing campaigns. These actors set up operational infrastructure to obfuscate their source infrastructure, host domains and malware for targeting organizations, establish command and control nodes, and harvest credentials and other valuable information from their targets.

In summer 2015, an APT29 spearphishing campaign directed emails containing a malicious link to over 1,000 recipients, including multiple U.S. Government victims. APT29 used legitimate domains, to include domains associated with U.S. organizations and educational institutions, to host malware and send spearphishing emails.

In the course of that campaign, APT29 successfully compromised a U.S. political party. At least one targeted individual activated links to malware hosted on operational infrastructure of opened attachments containing malware. APT29 delivered malware to the political party’s systems, established persistence, escalated privileges, enumerated active directory accounts, and exfiltrated email from several accounts through encrypted connections back through operational infrastructure. In spring 2016, APT28 compromised the same political party, again via targeted spearphishing. This time, the spearphishing email tricked recipients into changing their passwords through a fake webmail domain hosted on APT28 operational infrastructure. Using the harvested credentials, APT28 was able to gain access and steal content, likely leading to the exfiltration of information from multiple senior party members. The U.S. Government assesses that information was leaked to the press and publicly disclosed.

Actors likely associated with RIS are continuing to engage in spearphishing campaigns, including one launched as recently as November 2016, just days after the U.S. election.

Color me ignorant, but does anyone see actual proof in this report?

Comments »

ESCALATION: Obama Order Expulsion of Russian Diplomats, Closure of Russian Facilities, and a Harsh Chastising

John Podesta’s gmail password was P@ssword because he’s a god damned idiot. Everyone had access to his emails, a litany of perfidy that proved the DNC and Democratic party was as corrupt as the winters in Siberia are cold. Whether those revelations cost Hillary Clinton the election is up for debate. No one really knows the actual ramifications of them and most people outside of political circles and internet trolls had no idea what Podesta’s emails contained — let alone how it connected to Clinton.

But our government believes, without a shadow of a doubt, Russia was behind the hacks — despite not showing the public any evidence to support said claims.

With just 21 days until kicked out of the White House, President Obama announced he was taking punitive actions against Russia — targeting 6 individuals and 5 Russian entities, as well as expelling 35 diplomats and the closure of two Russian compounds on US soil.

Bear in mind, we’ve targeted specific Russians and entities before.

Source: CNN

“Russia’s cyberactivities were intended to influence the election, erode faith in US democratic institutions, sow doubt about the integrity of our electoral process, and undermine confidence in the institutions of the US government,” the statement said. “These actions are unacceptable and will not be tolerated.”

According to statements from the White House and the Treasury Department, the government has sanctioned nine entities and individuals: the GRU and the FSB, two Russian intelligence services; four individual officers of the GRU; three companies that provided material support to the GRU’s operations; and two Russian individuals for using cyber-enabled means to cause misappropriation of funds and personal identifying information.

Obama also said in the statement announcing that the diplomats have been ordered to leave the country, that those individuals and their families were given 72 hours to leave the United States.

“These actions follow repeated private and public warnings that we have issued to the Russian government, and are a necessary and appropriate response to efforts to harm U.S. interests in violation of established international norms of behavior,” Obama said in the statement.

Here is the full statement.

Statement by the President on Actions in Response to Russian Malicious Cyber Activity and Harassment

Today, I have ordered a number of actions in response to the Russian government’s aggressive harassment of U.S. officials and cyber operations aimed at the U.S. election. These actions follow repeated private and public warnings that we have issued to the Russian government, and are a necessary and appropriate response to efforts to harm U.S. interests in violation of established international norms of behavior.

All Americans should be alarmed by Russia’s actions. In October, my Administration publicized our assessment that Russia took actions intended to interfere with the U.S. election process. These data theft and disclosure activities could only have been directed by the highest levels of the Russian government. Moreover, our diplomats have experienced an unacceptable level of harassment in Moscow by Russian security services and police over the last year. Such activities have consequences. Today, I have ordered a number of actions in response.

I have issued an executive order that provides additional authority for responding to certain cyber activity that seeks to interfere with or undermine our election processes and institutions, or those of our allies or partners. Using this new authority, I have sanctioned nine entities and individuals: the GRU and the FSB, two Russian intelligence services; four individual officers of the GRU; and three companies that provided material support to the GRU’s cyber operations. In addition, the Secretary of the Treasury is designating two Russian individuals for using cyber-enabled means to cause misappropriation of funds and personal identifying information. The State Department is also shutting down two Russian compounds, in Maryland and New York, used by Russian personnel for intelligence-related purposes, and is declaring “persona non grata” 35 Russian intelligence operatives. Finally, the Department of Homeland Security and the Federal Bureau of Investigation are releasing declassified technical information on Russian civilian and military intelligence service cyber activity, to help network defenders in the United States and abroad identify, detect, and disrupt Russia’s global campaign of malicious cyber activities.

These actions are not the sum total of our response to Russia’s aggressive activities. We will continue to take a variety of actions at a time and place of our choosing, some of which will not be publicized. In addition to holding Russia accountable for what it has done, the United States and friends and allies around the world must work together to oppose Russia’s efforts to undermine established international norms of behavior, and interfere with democratic governance. To that end, my Administration will be providing a report to Congress in the coming days about Russia’s efforts to interfere in our election, as well as malicious cyber activity related to our election cycle in previous elections.

Naturally, Republican shill, Paul Ryan, supports these measures.

Schumer agrees with Ryan

Comments »

Sears Kept Alive by its CEO, Eddie Lampert, Again

It looks like Eddie Lampert isn’t quite done with Sears yet. I remember when he was the genius that was going to turn around K-Mart, based solely on its real estate holdings. Then they merged with Sears and Eddie was going to change the retail landscape. After all, this is a man who negotiated his own release from gun-wielding kidnappers after 30hrs and turned Autozone into the powerhouse it is today.

Truth be told, as fun as it is to demonize Eddie for the failures at both Sears and Kmart, there was little he could do — as the Amazon juggernaut does not discriminate and destroys all in its path.

Today he announced he’d lend another $200m to the struggling retailer — which ups his loans to more than $800m over the past two years. Naturally, the debt is collateralized against somewhat lucrative real estate holdings and I’m sure Eddie will find a way to make it work for him. But, from a PR standpoint, as CEO of the company, this is an unmitigated, fucking, disaster.

shld2

shld

These losses are caused by disastrous same store sales — which recently dropped by 7.4% (-10% at Sears and -4.4% at Kmart)

The majority of Sears’ debt is coming due in 2020, at which point the bedraggled retailers will likely be put to rest.
shld4

Source: Bloomberg

In a statement on the loan, Sears CFO Jason Hollar said: “As Sears Holdings has consistently shown, we will take actions to adjust our capital structure, generate liquidity, and manage our business to enable us to execute on our transformation while meeting all of our financial obligations. This new standby letter of credit facility further demonstrates that Sears Holdings has numerous options to finance our business strategy.”

In addition to lending money to Sears, Eddie is also providing REIT spinoff, Seritage Growth Properties, with a $200 line of credit.

Anyone else want some money? Eddie is in a generous mood.


Comments »