iBankCoin
Home / 2016 (page 2)

Yearly Archives: 2016

DRUDGE REPORT HIT WITH MASSIVE DDOS ATTACK; MATT DRUDGE PONDERS IF GOVERNMENT WAS BEHIND ATTACK

Drudgereport.com was the number 1 source of information during the elections. It was and always has been, or at least for the past decade or so, the single most popular destination for news — especially during elections. On the same day that the Obama administration announced sanctions again Russia, Drudge goes down.

Coincidence?

Drudge ponders aloud on Twitter.

down

One of my favorite interviews ever was when Drudge showed up to the Alex Jones show for a chat.

Comments »

Attention Exodus Members: The New GARP Index Has Been Launched

Pardon the late night, late year self-indulgence. We do need to keep the champagne flowing around here and have worked very hard at keeping Exodus a top tier information tool for investors. I just launched the new GARP index for the first half of 2017 and it’s probably my boldest yet. I can’t give any details away to non-members, since your sort do not possess such privileges, but just know that I placed a lot of effort behind it.

As God is my witness, it will likely return -100% over the next six months. Nonetheless, I’ve prepared myself for extreme winship in 2017. After a year traveling the seven seas in an ark filled with gay giraffes and attack cobras, I’ve earned the right, by natural law, to return to my former glory and grace — imbued with the powers of 10,000 men and the brains of a billion — to set forth into the stock exchange and to remove the money from others and gently place it into my own pockets.

To all those interested in crossing my path, or to obstruct me in any way humanly possible, just know that I will crush and smother you — rip your skin from your skeletal bones — crown to toe — and then grind your bones into dust to be used in my summer gardens.

The GARP INDEX, gentlemen.

Comments »

Elysium: Chinese IPOs Returned Nearly 400% in First Month of Trading During 2016

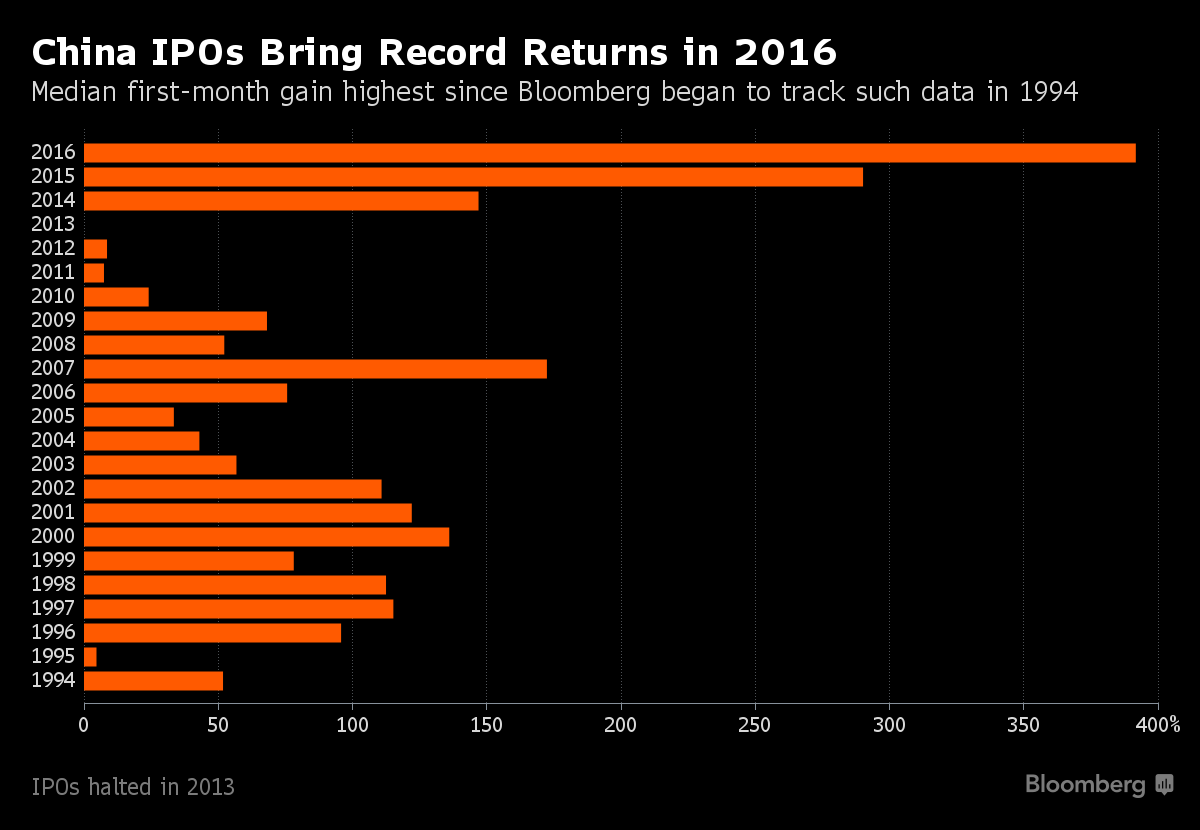
This is not as bubble, but a renaissance. The glorious Chinese people are adorned with the best of things — the prettiest and mightiest repurposed Soviet era aircraft carriers and the best stocks money could buy.

Over the course of 2016, mainland Chinese IPOs returned a mere 392% during the first month of trade — a mere pittance for such a wonderfully decadent society of dog eating swill drinkers.

It’s worth noting, the Chinese IPO market is a hard nut to crack. Similar to the United States, where preferred clientele at Goldman and JP Morgan get the bulk of the allocation, you have to be well connected and rich to get one in China. Bloomberg places the odds of getting an IPO at China 1 in 2,500, but I’m positive that’s a bullshit number — disseminated by enemy propaganda.

It’s much, much higher.

Two hundred and twenty six companies went public in China this year, the most since 2011, and the MEDIAN return was 392%.

The fuck out of here with this shit, right?

not-a-bubble

Meanwhile, the Shanghai sucked some major dick, off by 12%.

“In a weak market, speculators crowd into new shares where they believe selling pressure is low,” said Zhang Haidong, chief strategist at Jinkuang Investment Management in Shanghai.

Oh, you don’t say? That’s what happened, a flight to inequality so to say.

In case you’re wondering how in the world 226 stocks yielded a median return of 392%, the answer lies in the rules set forth by the government in Beijing. If you’re interested in tapping capital markets, you may not bring your company public unless it’s valuation is below 23x earnings. Where did such a precise number of 23x earnings come from? No one knows. Most likely from one of the whores or mistresses of any number of Chinese government officials.

The average IPO size was $106m. In other words, China’s ipo market is a rigged system of penny stock shit offerings.


Comments »

Russia Responds to Sanctions, says Obama’s ‘Aggressive Foreign Policy’ Designed to Hurt Trump

Under normal circumstances, the President-elect Trump and President Obama would discuss the proposed sanctions on Russia and issue a joint statement. After all, Obama doesn’t have to deal with the ramifications, Trump does. But in this fucked up political environment we live in, the incoming President and the one sitting in the White House agree on virtually nothing.

Obama and the democrats believe Russia won the election for Trump. As a matter of fact, many republicans like McCain and Ryan most likely believe the same. As such, we have a delicate situation playing out where Russia is being punished and publicly humiliated, in spite of the wishes of the President elect.

The spokesman for President Vladimir Putin says Moscow regrets the new sanctions that the Obama administration imposed on Russia on Thursday and is considering retaliatory steps.

Dmitry Peskov, spokesman for the Kremlin, said Obama’s actions were both “unpredictable” and “aggressive foreign policy.”

He furthered:

“Such steps of the U.S. administration that has three weeks left to work are aimed at two things: to further harm Russian-American ties, which are at a low point as it is, as well as, obviously, deal a blow on the foreign policy plans of the incoming administration of the president-elect.”

Peskov said Putin was working on methods to retaliate.

Konstantin Kosachev, head of the Kremlin’s upper house’s international affairs committee, told Interfax  Russia “needs to consider the circumstances of the transition period and a possible reaction of the U.S. president-elect.”


Comments »

The FBI and DHS Issue Report Showing Juvenile Evidence of Russian Hacking

Are they seriously going to claim this 3-page report proves Russia hacked our elections?

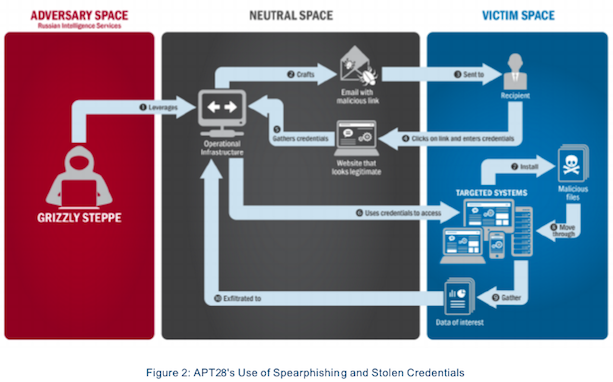
Here are the juicy details, highlighted by retarded graphics, showing ‘adversary, neutral, and VICTIM spaces.’ In this ‘report’, the government claims Russian agents, labeled APT28 and APT29, hacked into a US political party. These hackers, apparently, have a long track record of hacking into governments, universities, think tanks, and corporations — on a global scale.
proof

Previous JARs have not attributed malicious cyber activity to specific countries or threat actors. However, public attribution of these activities to RIS is supported by technical indicators from the U.S. Intelligence Community, DHS, FBI, the private sector, and other entities. This determination expands upon the Joint Statement released October 7, 2016, from the Department of Homeland Security and the Director of National Intelligence on Election Security. This activity by RIS is part of an ongoing campaign of cyber-enabled operations directed at the U.S. government and its citizens.

These cyber operations have included spearphishing campaigns targeting government organizations, critical infrastructure entities, think tanks, universities, political organizations, and corporations leading to the theft of information. In foreign countries, RIS actors conducted damaging and/or disruptive cyber-attacks, including attacks on critical infrastructure networks. In some cases, RIS actors masqueraded as third parties, hiding behind false online personas designed to cause the victim to misattribute the source of the attack. This JAR provides technical indicators related to many of these operations, recommended mitigations, suggested actions to take in response to the indicators provided, and information on how to report such incidents to the U.S. Government.

The U.S. Government confirms that two different RIS actors participated in the intrusion into a U.S. political party. The first actor group, known as Advanced Persistent Threat (APT) 29, entered into the party’s systems in summer 2015, while the second, known as APT28, entered in spring 2016.

Both groups have historically targeted government organizations, think tanks, universities, and corporations around the world. APT29 has been observed crafting targeted spearphishing campaigns leveraging web links to a malicious dropper; once executed, the code delivers Remote Access Tools (RATs) and evades detection using a range of techniques. APT28 is known for leveraging domains that closely mimic those of targeted organizations and tricking potential victims into entering legitimate credentials. APT28 actors relied heavily on shortened URLs in their spearphishing email campaigns.

Once APT28 and APT29 have access to victims, both groups exfiltrate and analyze information to gain intelligence value. These groups use this information to craft highly targeted spearphishing campaigns. These actors set up operational infrastructure to obfuscate their source infrastructure, host domains and malware for targeting organizations, establish command and control nodes, and harvest credentials and other valuable information from their targets.

In summer 2015, an APT29 spearphishing campaign directed emails containing a malicious link to over 1,000 recipients, including multiple U.S. Government victims. APT29 used legitimate domains, to include domains associated with U.S. organizations and educational institutions, to host malware and send spearphishing emails.

In the course of that campaign, APT29 successfully compromised a U.S. political party. At least one targeted individual activated links to malware hosted on operational infrastructure of opened attachments containing malware. APT29 delivered malware to the political party’s systems, established persistence, escalated privileges, enumerated active directory accounts, and exfiltrated email from several accounts through encrypted connections back through operational infrastructure. In spring 2016, APT28 compromised the same political party, again via targeted spearphishing. This time, the spearphishing email tricked recipients into changing their passwords through a fake webmail domain hosted on APT28 operational infrastructure. Using the harvested credentials, APT28 was able to gain access and steal content, likely leading to the exfiltration of information from multiple senior party members. The U.S. Government assesses that information was leaked to the press and publicly disclosed.

Actors likely associated with RIS are continuing to engage in spearphishing campaigns, including one launched as recently as November 2016, just days after the U.S. election.

Color me ignorant, but does anyone see actual proof in this report?

Comments »

ESCALATION: Obama Order Expulsion of Russian Diplomats, Closure of Russian Facilities, and a Harsh Chastising

John Podesta’s gmail password was P@ssword because he’s a god damned idiot. Everyone had access to his emails, a litany of perfidy that proved the DNC and Democratic party was as corrupt as the winters in Siberia are cold. Whether those revelations cost Hillary Clinton the election is up for debate. No one really knows the actual ramifications of them and most people outside of political circles and internet trolls had no idea what Podesta’s emails contained — let alone how it connected to Clinton.

But our government believes, without a shadow of a doubt, Russia was behind the hacks — despite not showing the public any evidence to support said claims.

With just 21 days until kicked out of the White House, President Obama announced he was taking punitive actions against Russia — targeting 6 individuals and 5 Russian entities, as well as expelling 35 diplomats and the closure of two Russian compounds on US soil.

Bear in mind, we’ve targeted specific Russians and entities before.

Source: CNN

“Russia’s cyberactivities were intended to influence the election, erode faith in US democratic institutions, sow doubt about the integrity of our electoral process, and undermine confidence in the institutions of the US government,” the statement said. “These actions are unacceptable and will not be tolerated.”

According to statements from the White House and the Treasury Department, the government has sanctioned nine entities and individuals: the GRU and the FSB, two Russian intelligence services; four individual officers of the GRU; three companies that provided material support to the GRU’s operations; and two Russian individuals for using cyber-enabled means to cause misappropriation of funds and personal identifying information.

Obama also said in the statement announcing that the diplomats have been ordered to leave the country, that those individuals and their families were given 72 hours to leave the United States.

“These actions follow repeated private and public warnings that we have issued to the Russian government, and are a necessary and appropriate response to efforts to harm U.S. interests in violation of established international norms of behavior,” Obama said in the statement.

Here is the full statement.

Statement by the President on Actions in Response to Russian Malicious Cyber Activity and Harassment

Today, I have ordered a number of actions in response to the Russian government’s aggressive harassment of U.S. officials and cyber operations aimed at the U.S. election. These actions follow repeated private and public warnings that we have issued to the Russian government, and are a necessary and appropriate response to efforts to harm U.S. interests in violation of established international norms of behavior.

All Americans should be alarmed by Russia’s actions. In October, my Administration publicized our assessment that Russia took actions intended to interfere with the U.S. election process. These data theft and disclosure activities could only have been directed by the highest levels of the Russian government. Moreover, our diplomats have experienced an unacceptable level of harassment in Moscow by Russian security services and police over the last year. Such activities have consequences. Today, I have ordered a number of actions in response.

I have issued an executive order that provides additional authority for responding to certain cyber activity that seeks to interfere with or undermine our election processes and institutions, or those of our allies or partners. Using this new authority, I have sanctioned nine entities and individuals: the GRU and the FSB, two Russian intelligence services; four individual officers of the GRU; and three companies that provided material support to the GRU’s cyber operations. In addition, the Secretary of the Treasury is designating two Russian individuals for using cyber-enabled means to cause misappropriation of funds and personal identifying information. The State Department is also shutting down two Russian compounds, in Maryland and New York, used by Russian personnel for intelligence-related purposes, and is declaring “persona non grata” 35 Russian intelligence operatives. Finally, the Department of Homeland Security and the Federal Bureau of Investigation are releasing declassified technical information on Russian civilian and military intelligence service cyber activity, to help network defenders in the United States and abroad identify, detect, and disrupt Russia’s global campaign of malicious cyber activities.

These actions are not the sum total of our response to Russia’s aggressive activities. We will continue to take a variety of actions at a time and place of our choosing, some of which will not be publicized. In addition to holding Russia accountable for what it has done, the United States and friends and allies around the world must work together to oppose Russia’s efforts to undermine established international norms of behavior, and interfere with democratic governance. To that end, my Administration will be providing a report to Congress in the coming days about Russia’s efforts to interfere in our election, as well as malicious cyber activity related to our election cycle in previous elections.

Naturally, Republican shill, Paul Ryan, supports these measures.

Schumer agrees with Ryan

Comments »

Sears Kept Alive by its CEO, Eddie Lampert, Again

It looks like Eddie Lampert isn’t quite done with Sears yet. I remember when he was the genius that was going to turn around K-Mart, based solely on its real estate holdings. Then they merged with Sears and Eddie was going to change the retail landscape. After all, this is a man who negotiated his own release from gun-wielding kidnappers after 30hrs and turned Autozone into the powerhouse it is today.

Truth be told, as fun as it is to demonize Eddie for the failures at both Sears and Kmart, there was little he could do — as the Amazon juggernaut does not discriminate and destroys all in its path.

Today he announced he’d lend another $200m to the struggling retailer — which ups his loans to more than $800m over the past two years. Naturally, the debt is collateralized against somewhat lucrative real estate holdings and I’m sure Eddie will find a way to make it work for him. But, from a PR standpoint, as CEO of the company, this is an unmitigated, fucking, disaster.

shld2

shld

These losses are caused by disastrous same store sales — which recently dropped by 7.4% (-10% at Sears and -4.4% at Kmart)

The majority of Sears’ debt is coming due in 2020, at which point the bedraggled retailers will likely be put to rest.
shld4

Source: Bloomberg

In a statement on the loan, Sears CFO Jason Hollar said: “As Sears Holdings has consistently shown, we will take actions to adjust our capital structure, generate liquidity, and manage our business to enable us to execute on our transformation while meeting all of our financial obligations. This new standby letter of credit facility further demonstrates that Sears Holdings has numerous options to finance our business strategy.”

In addition to lending money to Sears, Eddie is also providing REIT spinoff, Seritage Growth Properties, with a $200 line of credit.

Anyone else want some money? Eddie is in a generous mood.


Comments »

Duterte of the Phillipines Slams US Ambassador, Claims He Found ‘Blueprint to Destabilize’ His Country Amongst His Belongings

The President of the Phillipines is, without question, a fucking lunatic. Just yesterday he threatened to toss corrupt politicians out of helicopters, suggesting he did it before. Today, he’s accusing Philip Goldberg, former Ambassador to the Phillipines, of having ‘blueprints’ to destabilize his government.

Source: RT

President Rodrigo Duterte said all ambassadors play a part in their respective countries’ spying operations, but American ambassadors have a “forte” for undermining the government of their host countries.

“Most of the ambassadors of the United States, but not all, are not really professional ambassadors. At the same time they are spying, they are connected with the CIA,” Duterte said in an interview with CNN Philippines.

Citing a document received from a “highly placed source,” the newspaper said that Goldberg’s “blueprint to undermine Duterte” included supporting domestic opposition with grants and diplomatic assistance, pressuring other South Asian nations politically and economically to cut ties with the Philippines, and targeting the president’s supporters to alienate them.

The US on Thursday denied such a plan existed, but Duterte said this sounded plausible, considering how Goldberg had been expelled as ambassador to Bolivia in 2008. Leftist President Evo Morales accused the American diplomat of siding with his rightist opponents and of orchestrating street protests and gave him 72 hours to leave the country.

Speaking of the alleged destabilization plan, the Philippine president said: “You might be able to oust me, but I will give you a bloody nose.”

Duterte has been on bad terms with Goldberg for quite some time. On one occasion he infamously called the American envoy a “gay son of a bitch” for interfering with Philippines politics.

If alive, General McCarthur would slap the shit out of Duterte.

Comments »

Gold Stocks Explode Higher After China Slashes Dollar Exposure in Renminbi Basket

China designed the renminbi CFETS basket as a way to peg the yuan against a variety of currencies to best represent their trading partners. In a surprise move last night, they slashed their dollar exposure from 26.4% to 22.4%, perhaps indicating less dependence on US markets for their goods. In the past analysts viewed this scheme as an indicator of further yuan weakness.

Here’s the new CFETS basket.

img_5959

Today’s result, however, is a sharply lower dollar and fast rising gold and silver prices.

img_5960

Gold miners are sharply higher, bouncing after months of underperformance.
img_5956

In case you’re wondering about gold, seasonally speaking, both January and February are, traditionally, the best times to own them.

img_5957

Valuation wise, the sector is a little elevated. But when comparing it to previous years when gold was running higher, current valuations are nowhere near stretched.

img_5958

The fate of the yellow metal is one embedded in the minds of investors. If people feel insecure about things, gold, typically, will trade higher. Or, if the Fed signals they won’t hike rates, investors will sell off dollars and bid up precious metals. Perhaps the market is being logical today, forecasting a trade war with China — which would definitely cause GDP to slow in the interim and cause Central Banks to meddle in our affairs again?

Somehow I doubt the ADD addled minds of traders are thinking that far ahead.

Comments »

Chinese Professor Writing for Pine River Capital Says China Will Win Trade War with America

The shills over at the Minnesota based hedge fund, Pine River, are making the media rounds these evening, after issuing a letter featuring a Hong Kong Professor named James Wang who said China would defeat the United States in a trade war. The entire article is suspect and wreaks of enemy propaganda.

Have a look, penned by <<<Bei Hu>>> (hmm).

This is what Wang had to say about a prospective trade war with the US,  which includes Trump slapping the shit out of China with 45% tariffs.

“By design, decision-makers in a democracy face difficulties coordinating a relief effort and must eventually face a political backlash from impacted domestic producers,” Wang wrote. “On this basis, the Chinese may have more runway to play the long game in a trade war.”

“The balance of power worldwide is much more diffuse compared to the early 20th century, and players like China and India have emerged to create new political centers of gravity,” Wang wrote. “However, as economic and political paralyses spread across the developed world, the most likely outcome is a trade war.”

In other words, Pine Capital believes America is finished and the balance of power now lies in Beijing.

The math, however, tells a different story, as China enjoys nearly a $300 billion per annum trade surplus with the United States, wholly dependent on the US consumer to keep their bedraggled populace at bay, saddled with incredibly high levels of debt (250%+) and soaring NPLs.

trade

Goldman analyst, Kinger Lau, believes punitive tariffs will clown-rape China’s GDP by 3% in 2017. Kevin Lau from Daiwa Capital isn’t as optimistic as Goldman. He thinks an American-Sino trade war will result in an 87% drop in Chinese exports to the US — a drop of $420 billion. That would equate to a 4.85% blow to the Chinese parasitical ‘economy.’

Even in a Trump light environment of just 15% tariffs, Chinese GDP stands to drop by 1.8%, according to Daiwa.

China’s protest would involve selling US treasuries, which have proven to be meaningless with QE programs and they might give Boeing, Ford and GM the boot. They might shut down a few disgusting KFC restaurants too.

Bottom line: Investors freak the fuck out when China misses by one tenth of one percent. Can you imagine if Chinese exports dropped by $420 billion or 87%?

Pain.

Comments »